 NOULI
How they work together
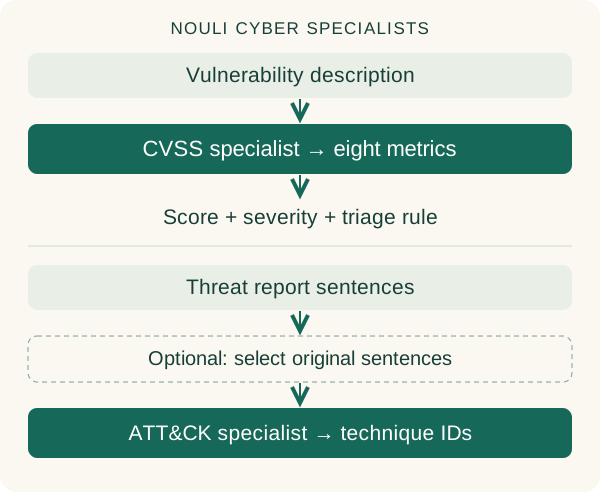
Use the specialist that matches your task. CVSS predicts eight base metrics; code calculates the score, severity and example triage route. ATT&CK suggests techniques supported by report text. The optional selector chooses original sentences before ATT&CK mapping. Nouli can connect these answers to rules and record the resulting workflow.
Models at a glance
| Component | Input → output |
|---|---|
| CVSS triage | Vulnerability description → CVSS v3.1 vector, score, severity and route |
| ATT&CK mapping | Behavior description → probabilities and suggestions across 49 technique labels |
| Optional source selector | Report sentences → references to selected original sentences |
The decision specialists run locally on CPU or CUDA. The optional selector requires CUDA and a separate public base download. No hosted API key is required.
Example inputs and outputs
CVSS triage
Input: “A remote unauthenticated attacker can exploit the vulnerability without user interaction to read or modify application data.”
Recorded output (probabilities and trace fields omitted):
{
  "vector": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N",
  "base_score": 8.2,
  "severity": "HIGH",
  "route": "prioritize"
}
The bundled routing rule prioritizes high or critical findings with network access, no privileges and no user interaction. Adapt that rule to your workflow.
ATT&CK mapping
Input: “The malware logs keystrokes, takes screenshots, collects files from the local system and exfiltrates the collected data over its existing command-and-control channel.”
Recorded output (probabilities and trace fields omitted):
{
  "threshold": 0.45,
  "techniques": ["T1005", "T1041", "T1056.001", "T1113"]
}
These correspond to Data from Local System, Exfiltration Over C2 Channel, Keylogging and Screen Capture. Both examples were run with the supplied weights on CPU. Complete inputs and outputs.
Quickstart
Use Python 3.12 and the HF CLI. Download the complete repository:
hf download nouli-ai/nouli-cyber-specialists --revision v1.0.0 --local-dir ./nouli-cyber-specialists
cd nouli-cyber-specialists
python3.12 -m venv .venv
.venv/bin/python -m pip install -r requirements-inference.txt
.venv/bin/python scripts/infer.py --bundle . --task cvss --device cpu \
  --text "$(cat examples/cvss-input.txt)"
.venv/bin/python scripts/infer.py --bundle . --task tram --device cpu \
  --text "$(cat examples/tram-input.txt)"
Keep the repository together: its checkpoints use the supplied custom loader. See setup and Nouli integration for CUDA, source selection, offline use and the native CVSS workflow.
Base models and data
CVSS uses ModernBERT; ATT&CK combines SecureBERT 2.0 and CTI-BERT. The optional selector is an adapter for Qwen3-4B-Instruct-2507.
Data sources are CVSS31Vectors and TRAM ATT&CK Multilabel Clean. Pinned source revisions and notices accompany the release.
Limitations
- English text only; suggestions need analyst review. These models do not inspect code or establish that a system is secure.
- CVSS estimates are not authoritative vulnerability scores. ATT&CK coverage is limited to the 49 bundled labels; an empty result does not mean benign behavior.
- Long inputs are truncated to the documented limits. Source selection is optional and can omit useful evidence.
License and citation
Apache-2.0; upstream and data notices apply. See NOTICE and licenses. CVSS is owned by FIRST and used by permission. ATT&CK® is a registered trademark of The MITRE Corporation.
Nouli AI. Nouli Cyber Specialists. Cite the published version and commit.